English
Audit log
The audit log keeps every action: sign-ins, ticket changes, assignments, approvals, role changes, asset movements and more. Each event is chained to the previous one with a cryptographic fingerprint, so an altered or deleted event is detected.
Where it is: Compliance → Audit log. Each record also has its own Activity section. Who sees it: with read activity you caused, your own; with read activity across your territories, your territories'. Exporting needs export the activity log. Plan: included in all. The full export and the chain verification report belong to the Audit export module (Enterprise). It's kept 90 days on Basic, 1 year on Pro and 7 years on Enterprise.
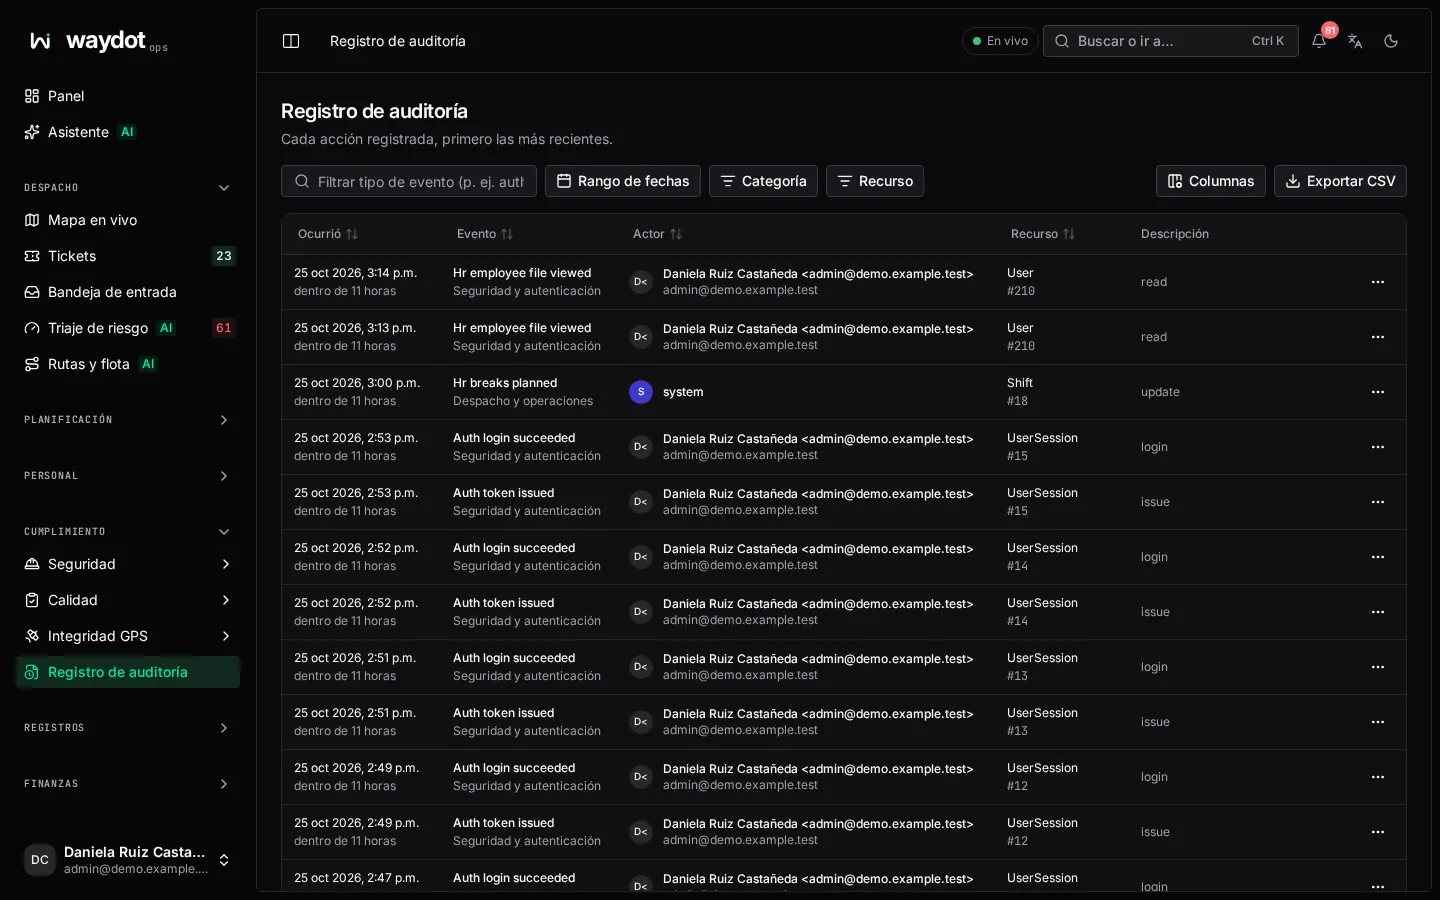
Columns
| Column | What it is |
|---|---|
| Date | When it happened. |
| Event | The type, for example auth.login, ticket.assigned. |
| Actor | Who did it, or System. |
| Category | Security & auth, Logistics & assets, Dispatch & operations or Master data. |
| Resource | What it's about: user, ticket, client, site, asset… |
Filters
- Filter event type (e.g. auth.login)...
- Category and Resource type.
If too many events match, This result set is large appears: narrow the filters or export the full set to review offline.
An event
Opening an event shows:
| Item | What it is |
|---|---|
| Event ID | Its identifier; Copy event ID. |
| Request ID | Groups the events of one action. |
| Source IP | Where it was done from. |
| Attribute changes | Before and After for each field. |
| Chain hash / SHA-256 | The fingerprint linking this event to the previous one. |
Exporting
Export CSV downloads the filtered events.